

Sub-GHz radio, LoRa and industrial links
We test the long-range, industrial and exotic radio behind remotes, sensors and machines: LoRa and LoRaWAN, proprietary sub-GHz links, undocumented protocols, and the devices that speak them.
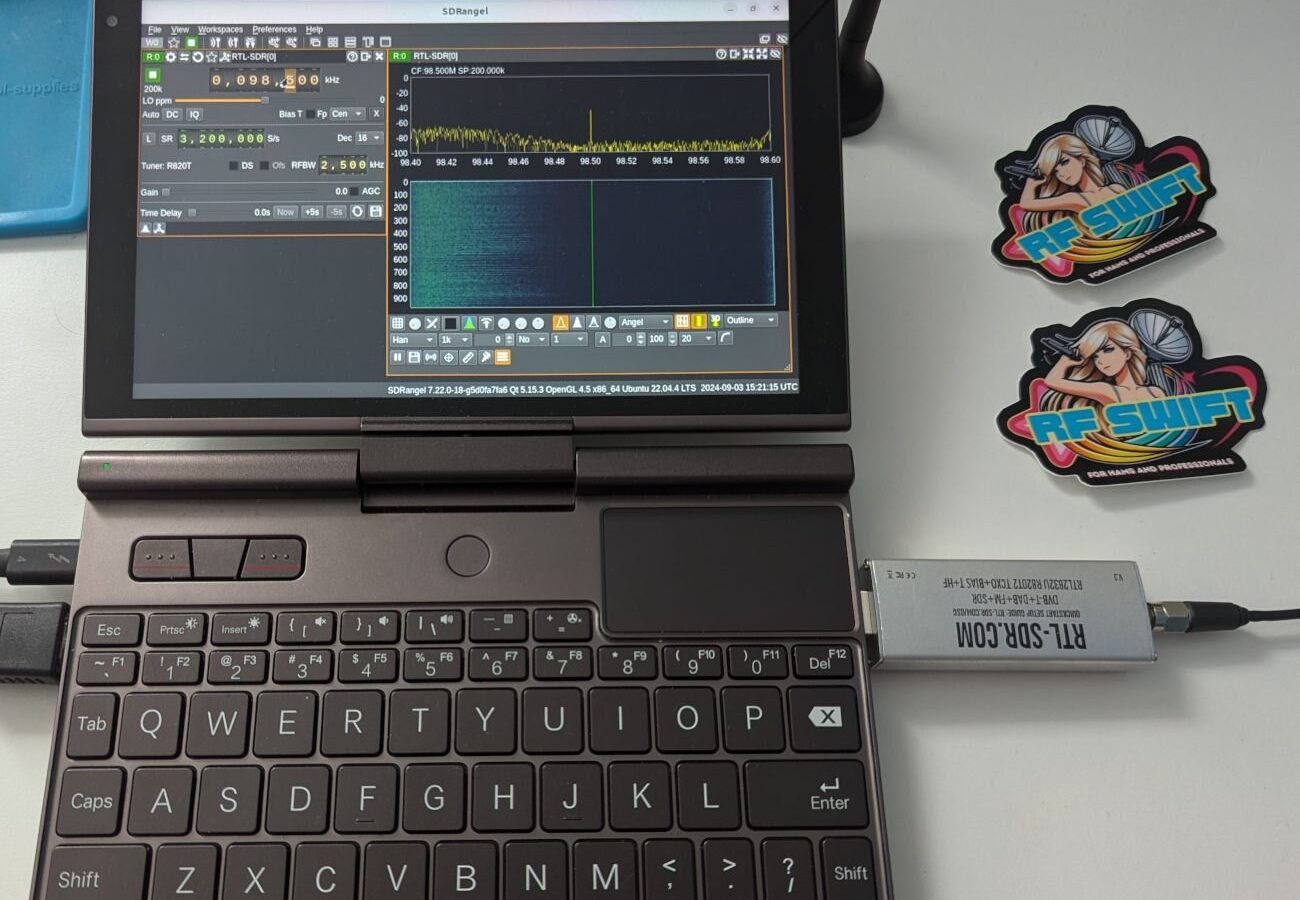
What an attacker could do
We check it before they do, with the same equipment.
Replay a remote
Capture and replay a remote to open a gate or trigger a device.
Spoof a sensor
Forge telemetry or commands that a receiver accepts as genuine.
Break LoRaWAN
Attack join procedures, keys and rate limiting.
Crack an exotic protocol
Reverse-engineer an undocumented radio link from the air, then read or forge what it carries.
What we test
- LoRa and LoRaWAN devices and gateways
- Proprietary sub-GHz remotes and sensors
- Industrial and exotic radio links, documented or not
- The devices and back-ends behind them
- The radio and LoRaWAN stacks in devices and gateways: we hunt for the bugs an attacker could use over the air to crash or take them over
LoRaWAN’s Protocol Stacks: The Forgotten Targets at Risk
Forced Entry: A Security Test for Automatic Garage Doors
RollD.O.R Attacks – Getting permanent accesses in garages
Protecting LoRaWAN Hardware from Attacks in the Wild
Gauging LoRaWAN Communication Security with LoRaPWN
LoRaPWNing: Practical Radio Attacks on LoRaWAN
Trainings on this subject
All trainings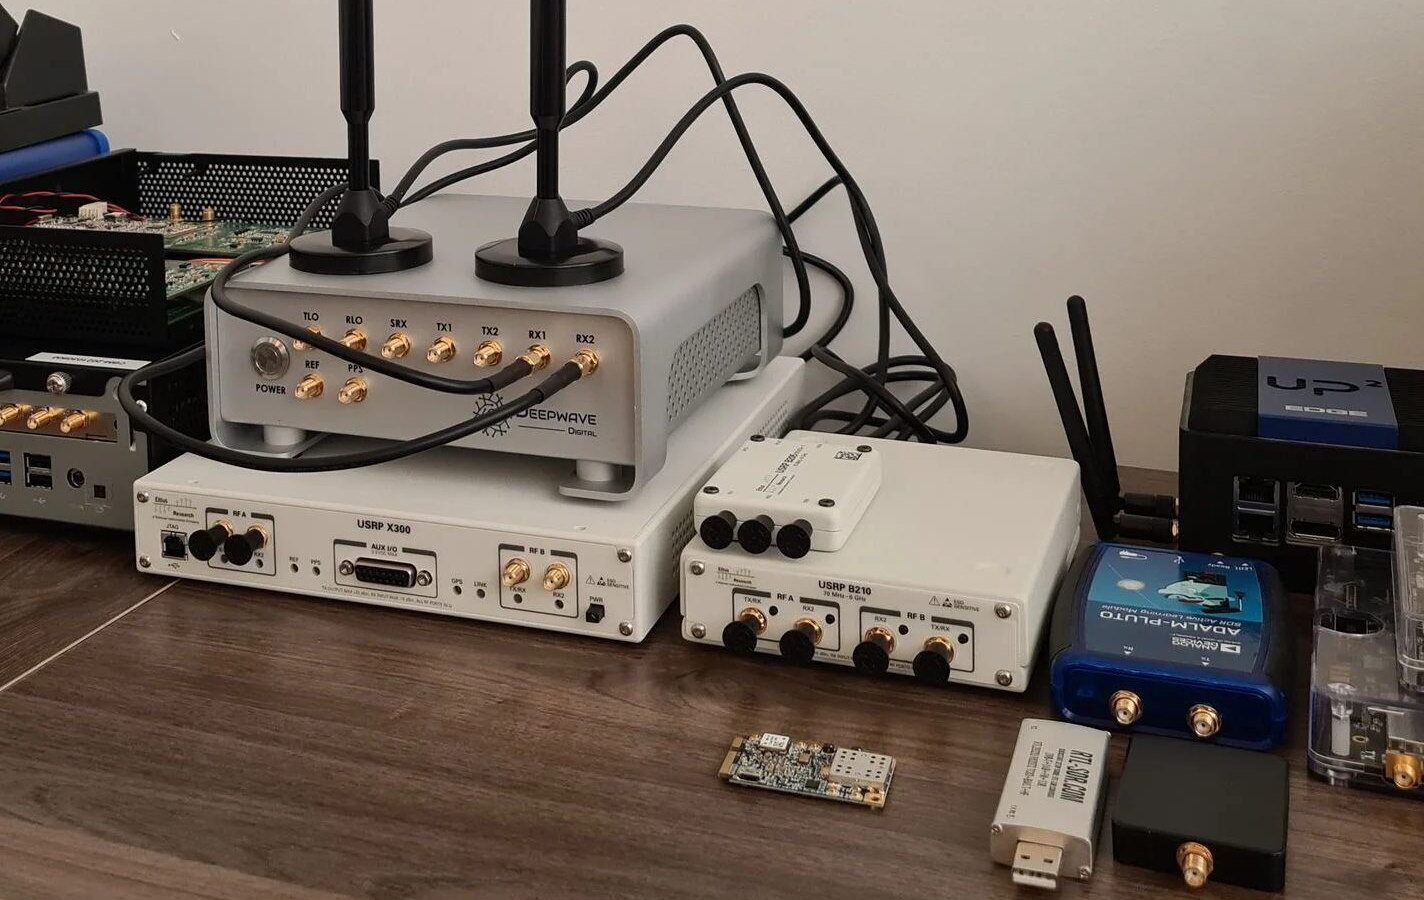
Four days on software-defined radio for security. Beyond running public tools, you learn how they work and build your own to analyse and attack systems, using real cases from our pentests and red team engagements, and the method to approach targets nobody has documented yet.
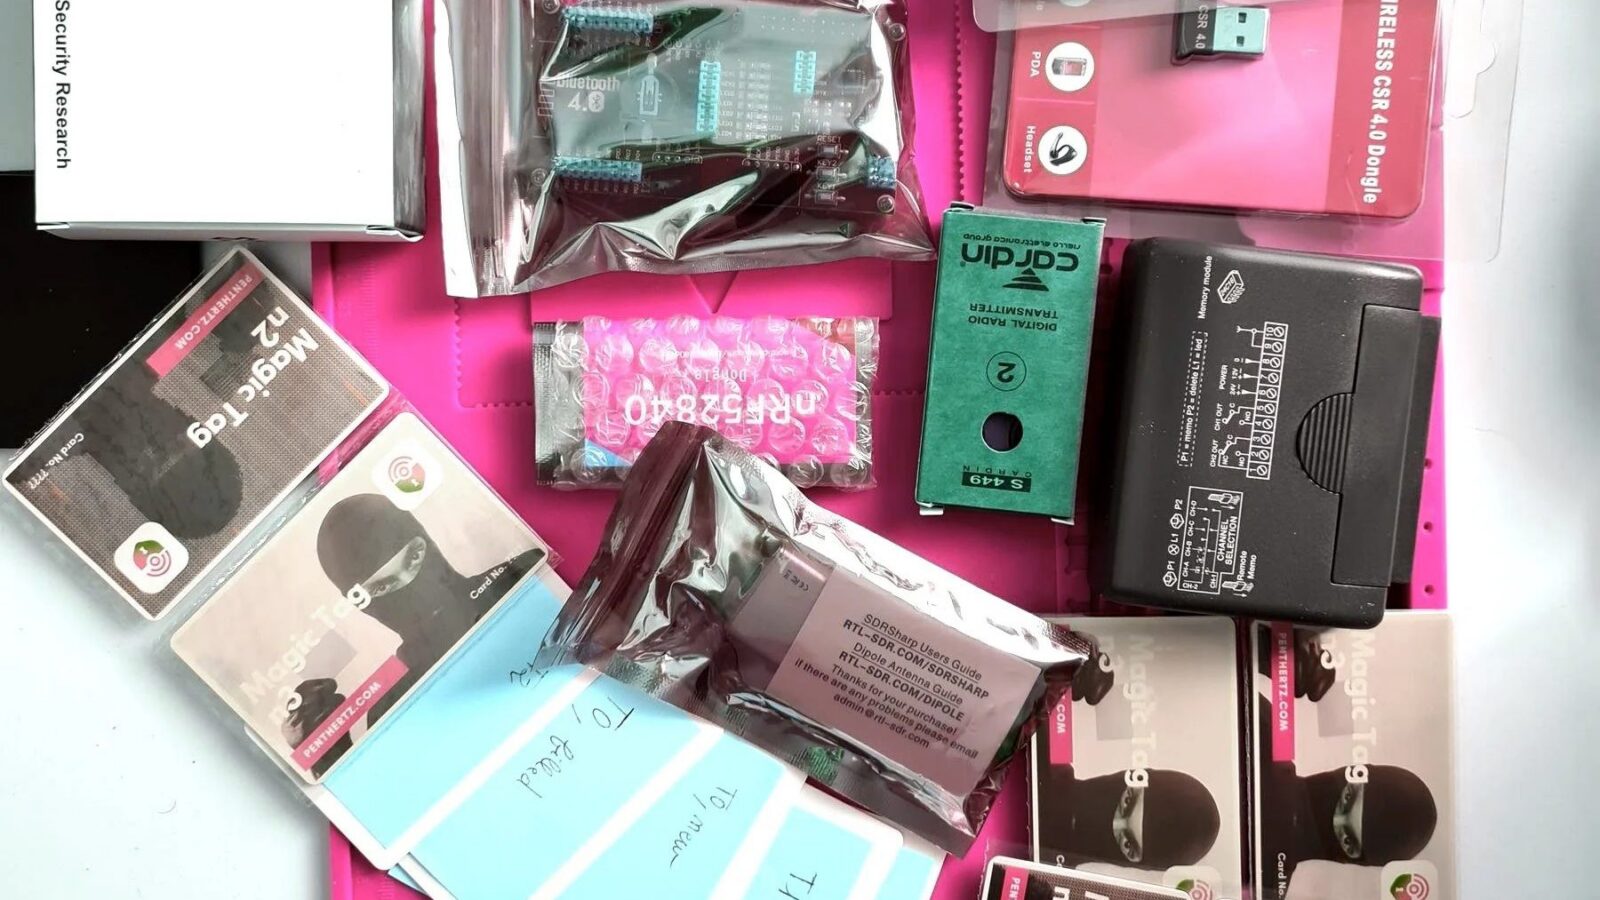
Three days on current attacks against the RFID, NFC, Bluetooth LE, nRF and sub-GHz systems met on pentests and red team engagements, to test access control and the radio links behind it.
Talk to us about your project
We scope the work in a first call, then send a fixed-price proposal: intrusion tests, vulnerability research, fuzzing, test benches, trainings. Offices near Paris, Monday to Friday, 9:00 to 19:00.