

Vehicle, V2X, V2G charging and GPS security
We test and attack the radio and buses in and around vehicles: key fobs, V2X, GPS, tyre sensors, the CAN bus reached over a radio path, and the vehicle-to-grid (V2G) link to the charging station.
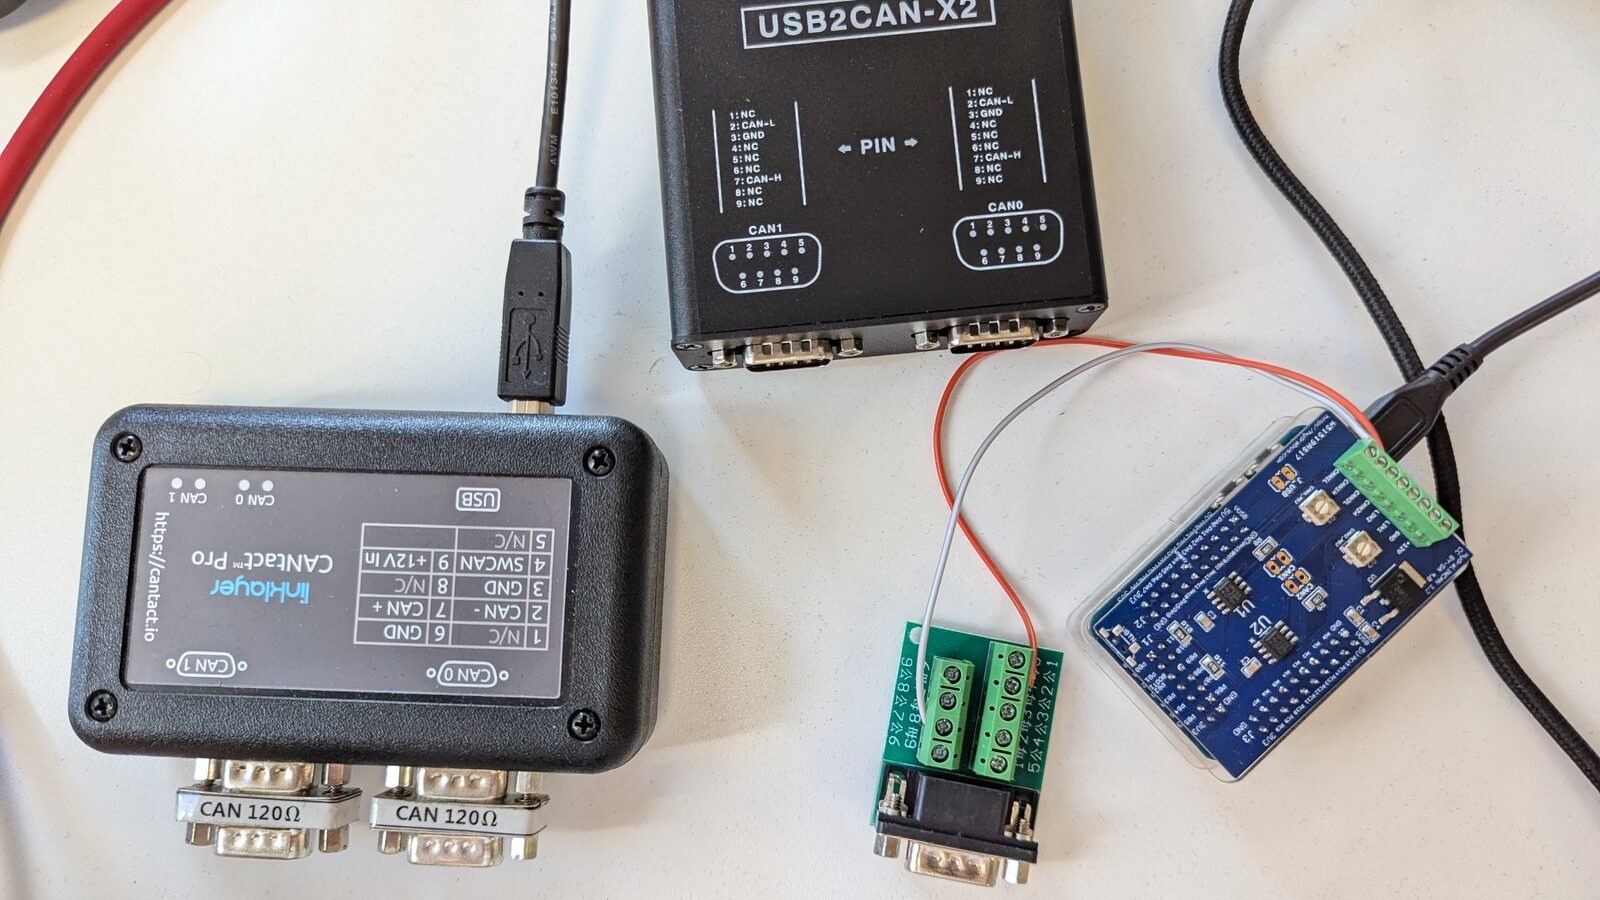
What an attacker could do
We check it before they do, with the same equipment.
Unlock and start
Relay or forge a key fob to open and start a vehicle.
Reach the bus
Get onto the vehicle bus through a radio interface.
Attack V2G charging
Abuse the vehicle-to-grid link (ISO 15118 over the power line) to hijack a charging session, or reach the charger and the vehicle behind it.
Spoof what the car trusts
Forge GPS positions, V2X messages or tyre-sensor data that the vehicle acts on.
What we test
- Key fobs and keyless entry
- V2X (DSRC and C-V2X) and telematics
- GPS and other GNSS receivers, against spoofing and jamming
- The CAN bus reached over radio
- EV charging and the vehicle-to-grid link (V2G, ISO 15118), from the vehicle side and the charger side
- The protocol stacks in ECUs, telematics units and chargers (CAN, V2X, ISO 15118): we hunt for the bugs an attacker could use to crash or take them over
Trainings on this subject
All trainingsNo public course on vehicle security yet: we build a tailored training for your team on key fobs, V2X, GPS and V2G charging.
Built around your stack: baseband fuzzing, Wi-Fi protocol stacks, advanced RFID and NFC with SDR, hardware attacks on embedded systems, and other technologies.
Talk to us about your project
We scope the work in a first call, then send a fixed-price proposal: intrusion tests, vulnerability research, fuzzing, test benches, trainings. Offices near Paris, Monday to Friday, 9:00 to 19:00.