

RF Swift, a containerised toolbox for SDR and RF security work
RF Swift is the containerised SDR toolbox we wrote to set up a working radio environment in one command. We use it on every engagement, attendees work with it in our trainings, and it is free and open source.
Quick setup
One command starts a container with the toolchain, drivers and dependencies already working together.
Reproducible
Versions are pinned, so a flowgraph written during a training still runs on the same image a year later.
Portable
Runs on a laptop with an SDR on USB. No lab, no server, no licence server.
Maintained
We use it on every engagement, so problems get fixed quickly.
What is inside
Tool versions are pinned so they work together, and a flowgraph from a training still runs a year later.
- GNU Radio
- With the blocks and out-of-tree modules we rely on
- Device drivers
- For the transceiver families listed below
- Analysis tooling
- Spectrum, demodulation and decoding utilities
- Mobile stacks
- Open-source components for 2G to 5G work
- RFID and sub-GHz
- Reader, cloner and transmit tooling
- Our flowgraphs
- The graphs and scripts used in the courses
Supported hardware
The families we use most. RF Swift supports much more hardware and many more tools: the full list is in the documentation.
| Device family | Notes |
|---|---|
| bladeRF (1.0, 2.0 micro) | Full duplex, the default in our kits and trainings |
| HackRF One | Half duplex, wide coverage, good first device |
| USRP (B and N series) | Lab-grade work, MIMO and higher sample rates |
| LimeSDR family | Full duplex, supported through SoapySDR |
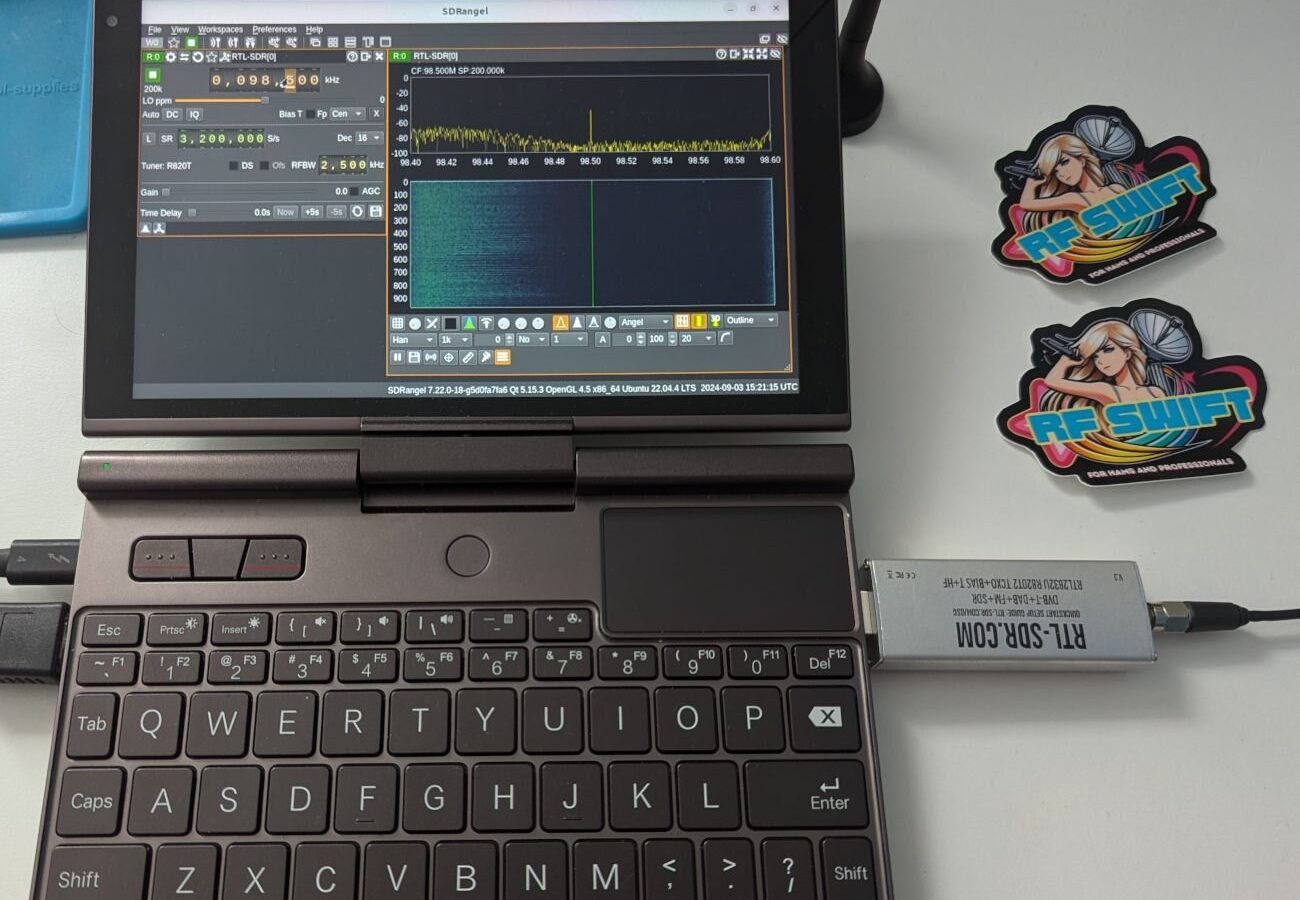
| RTL-SDR dongles | Receive only, enough for the introduction course |
| PlutoSDR | Compact full duplex, useful for travel setups |
Open-source tools and projects
GitHubStore sensitive files in the cloud or on shared media without trusting the host. A Rust encrypted-container tool with passphrase, FIDO2 (YubiKey, Titan, Nitrokey, Windows Hello), TPM 2.0 and hybrid post-quantum (ML-KEM-768 / 1024) keyslots. Mounts as a real drive on Linux, macOS and Windows.
RepositoryUniversal Radio Hacker Next Generation: investigate wireless protocols like a boss, and crack a few remotes.
RepositoryA Burp Suite extension that automates discovery, enumeration and exploitation of vulnerabilities in 5G Core Service-Based Interfaces.
RepositoryParses the 5G core OpenAPI 3.0 definitions the previous Burp extension could not, and generates requests for intrusion testing.
RepositoryZ-Wave packet interception and injection, rebuilt for Python 3 with S2 support and a modern Dear ImGui interface.
RepositoryReceive signals with an SDR, then decode and craft LoRaWAN packets on top of the gr-lora GNU Radio module.
RepositoryIntrude a Vehicle-to-Grid power-line network, and capture and inject V2G packets.
RepositoryScapy dissectors and tools to test power-line communication security: PLC discovery, key derivation, sniffing and PIB manipulation.
RepositoryMap 2G, 3G, 4G and other cellular networks in real life with a plain smartphone, like the osmocomBB monitoring feature.
RepositoryA smart jamming proof of concept for mobile equipment, driven by the Modmobmap tool.
RepositoryTalk to us about your project
We scope the work in a first call, then send a fixed-price proposal: intrusion tests, vulnerability research, fuzzing, test benches, trainings. Offices near Paris, Monday to Friday, 9:00 to 19:00.