

Give your team the RF and hardware skills to test in-house
Taught by the author of RF Swift, with the same tools we use on client engagements. Live sessions include a hardware kit. Penthertz is a registered French training organisation (no. 11788588278), so the courses can be funded as professional training.
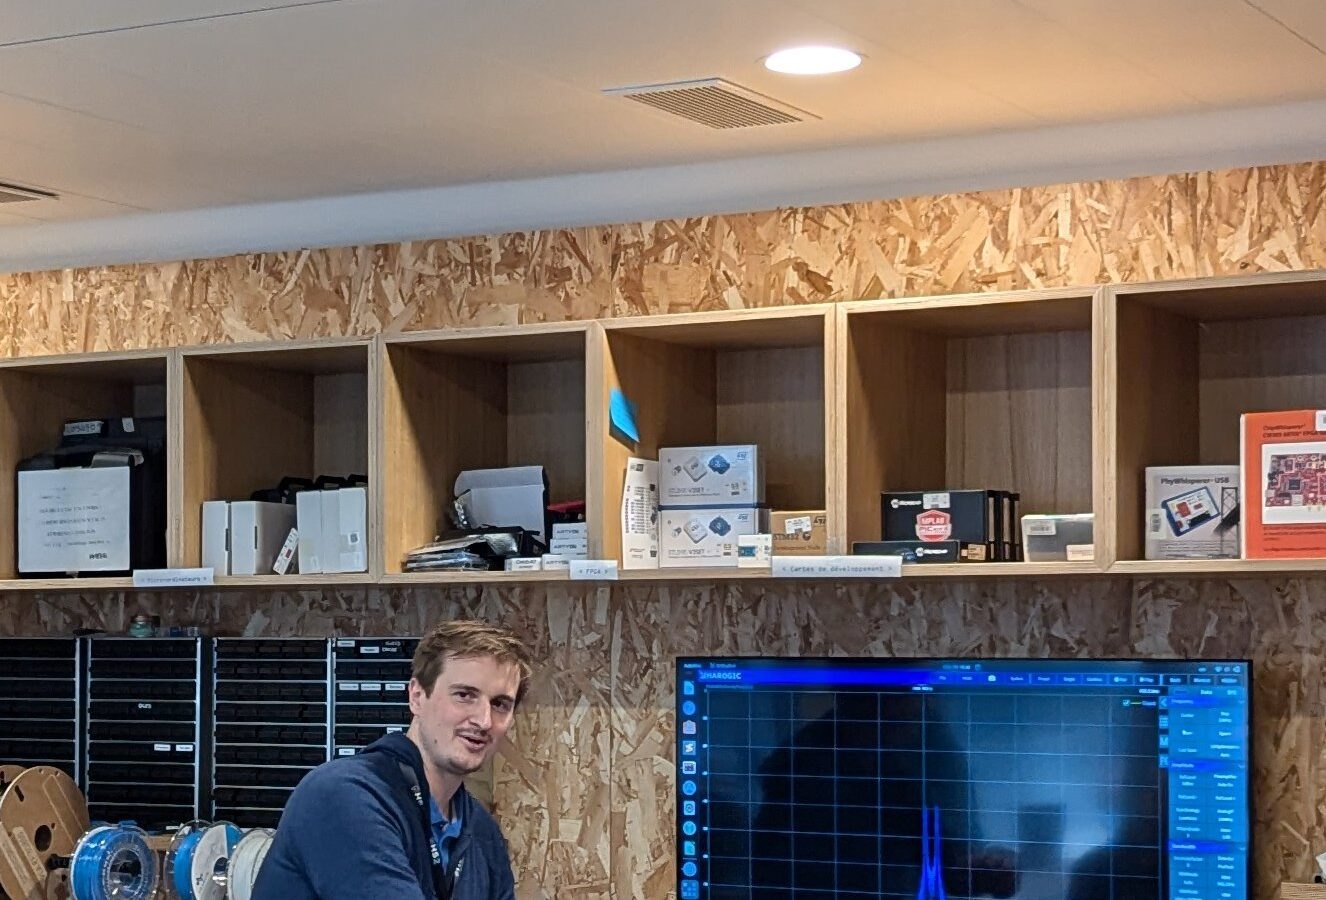
On your site or at a conference
Two to four days in a small group, hardware kit included. Also available remotely, with the kit sent in advance.
Hackademy courses, bought one at a time
Recorded courses you follow at your own pace, updated as the research moves on.
Built around your needs
Content based on your protocols, your hardware and your threat model. We scope it in a call and quote per group.
Registered training organisation
Penthertz is a registered French training organisation, no. 11788588278.
Funding
Ask us how to fund your team's training (company training plan and other schemes).
Accessibility
Have a disability or a specific need? Tell us when scoping and we will adapt the setup where we can.
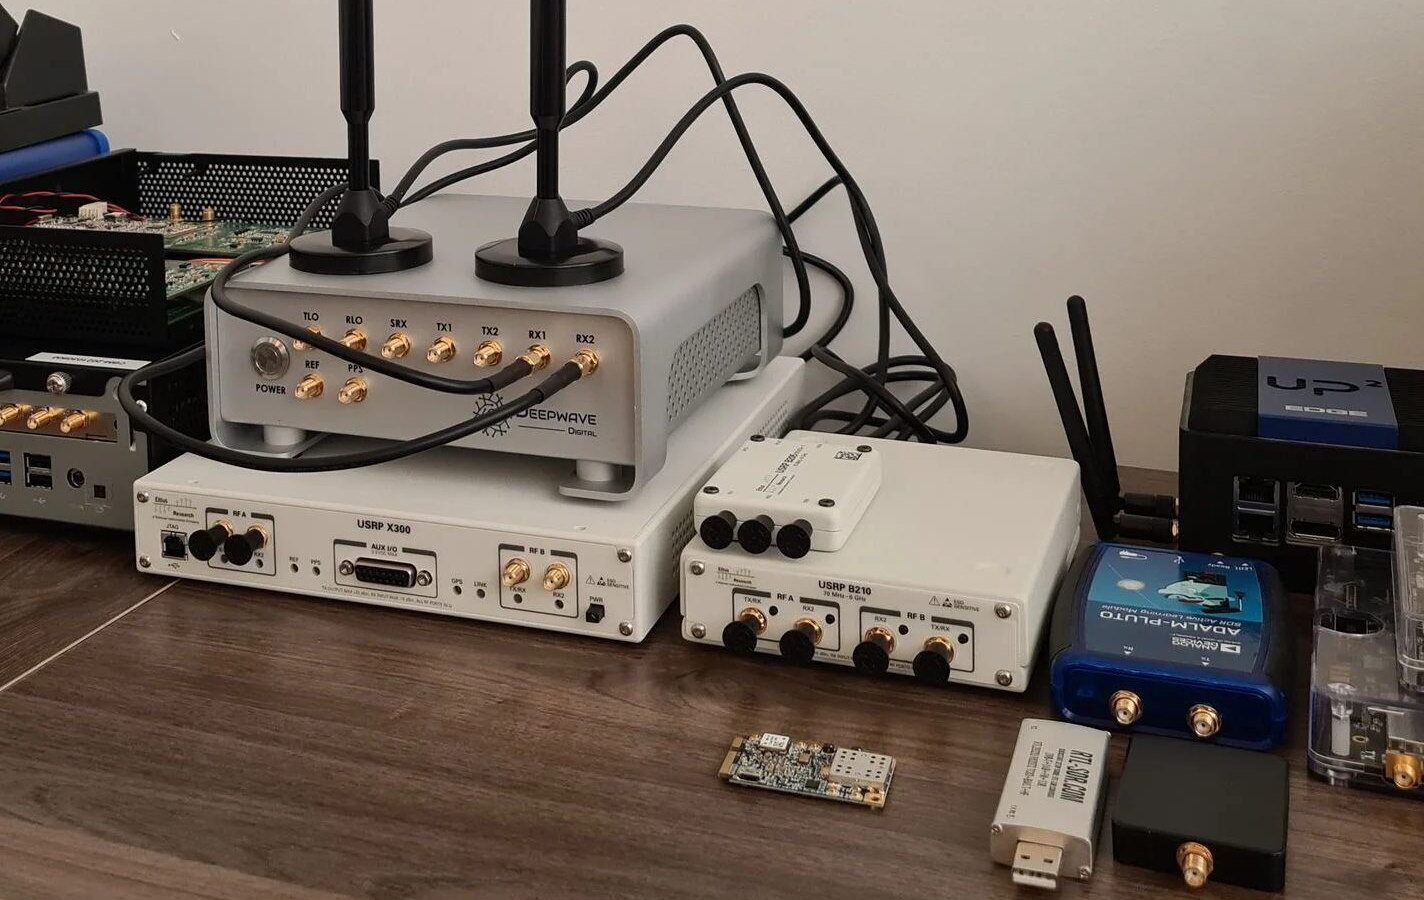
Four days on software-defined radio for security. Beyond running public tools, you learn how they work and build your own to analyse and attack systems, using real cases from our pentests and red team engagements, and the method to approach targets nobody has documented yet.
Three days assessing mobile devices and networks with software-defined radio. We demonstrate attacks in practice, mostly on user equipment but also on the core network, across phones, IoT modules, connected cars and infrastructure.
Three days on 5G NSA and SA security: assessing devices, the current and Next-Generation Core Network, and the attack surface OpenRAN brings. Private 5G on unlicensed bands puts campuses and companies on the air, and this course covers the new risks that come with it.
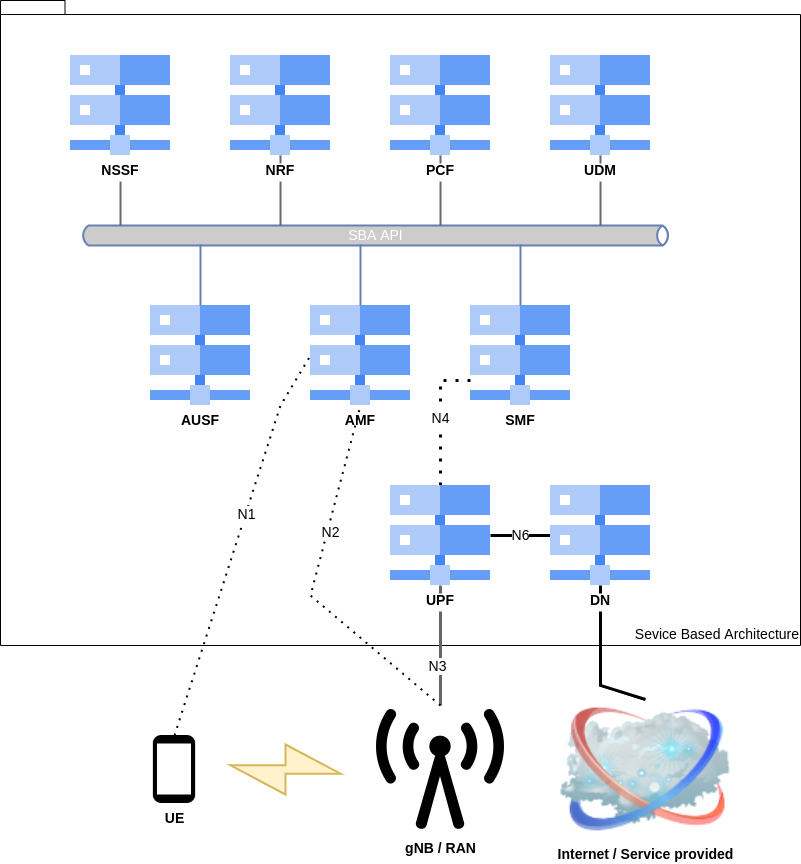
Three days on the weaknesses of operator core networks: the fundamentals, the interfaces and protocols, and what an attacker reaches from an internal pentest or from the outside during a Red Team. It also helps operators build their own measures by understanding the techniques.
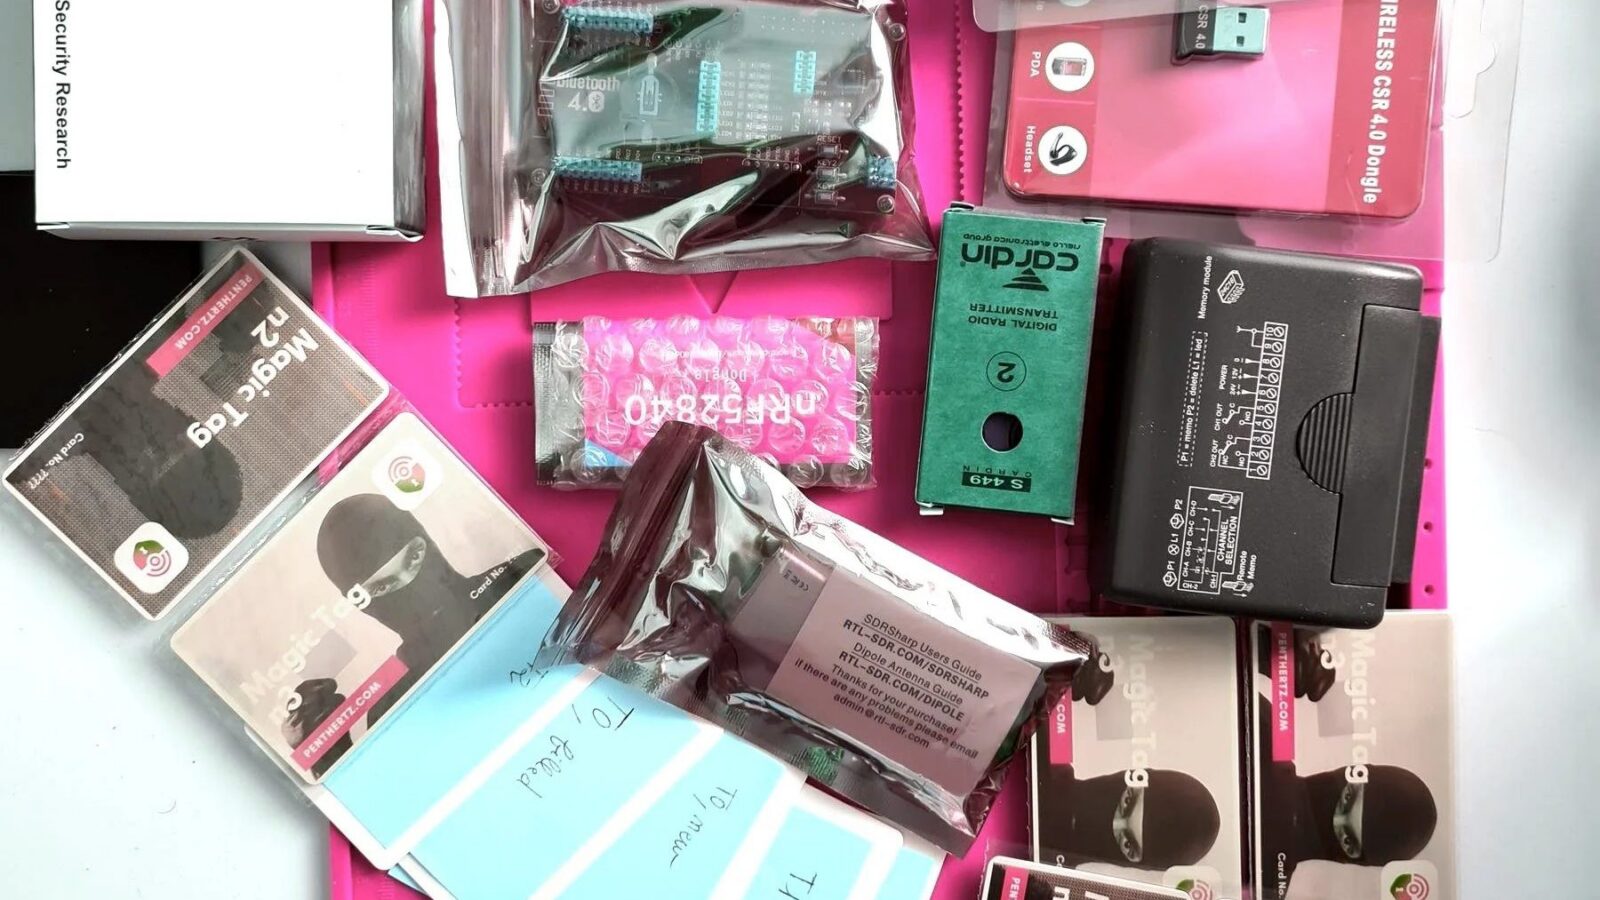
Three days on current attacks against the RFID, NFC, Bluetooth LE, nRF and sub-GHz systems met on pentests and red team engagements, to test access control and the radio links behind it.
Two days on current Wi-Fi assessment techniques, replacing outdated methods. You start with the basics of old and new attacks, then apply them against an organisation as in a red team engagement, based on our recent work.
The icebreaker to the software-defined radio world: how radio works, how to spot, capture and analyse a signal, and how to choose the right equipment, with quizzes and exercises on real captures.
Tired of obsolete RF tools, or of tools that do not fit your needs? Use GNU Radio to implement the features you need and build your own radio security tools, from simulation to real receivers and transmitters.
Hacking standard IoT devices with software-defined radio: the common attacks, the security mechanisms most IoT systems use, and ways to bypass them when possible.
Open doors stealthily with concrete techniques, and bypass most physical security systems that rely on RFID tags.
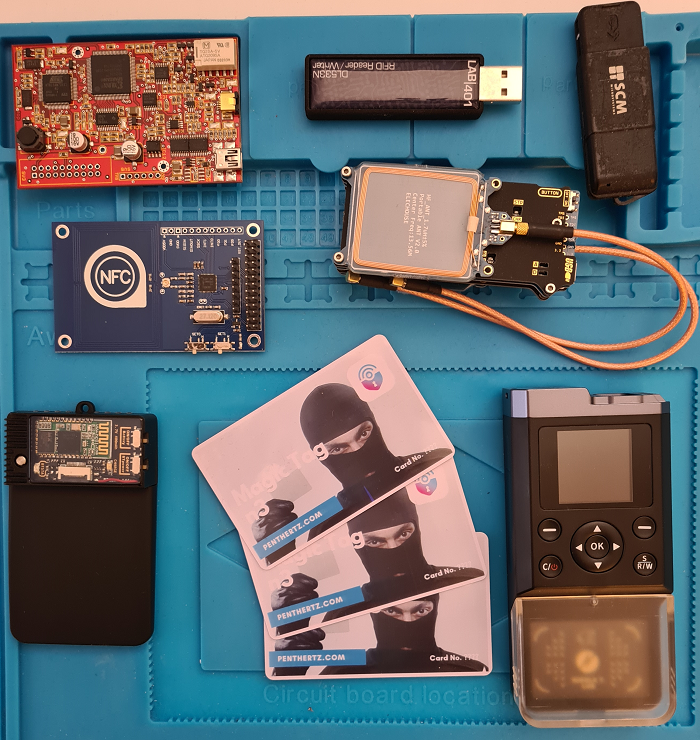
Going deeper with snooping communications: a short course on snooping MIFARE Classic exchanges with the Proxmark3, applied to the iCopy-X.
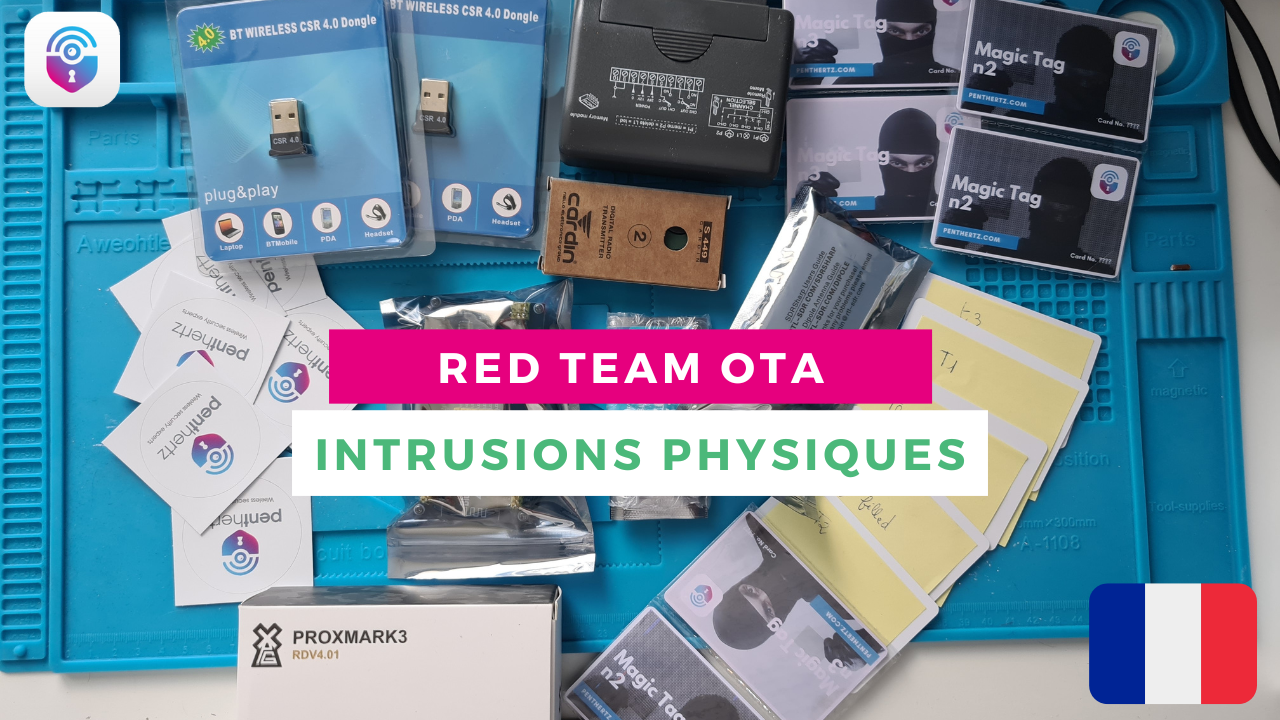
Dive into physical intrusion with the most modern radio attack techniques: RFID, Bluetooth LE, nRF and sub-GHz garage doors. Taught entirely in French.
Wi-Fi offensive attacks and countermeasures for red and blue teams: the modern ways to assess Wi-Fi networks, the right tools at the right moment, and practice on your own Wi-Fi target.
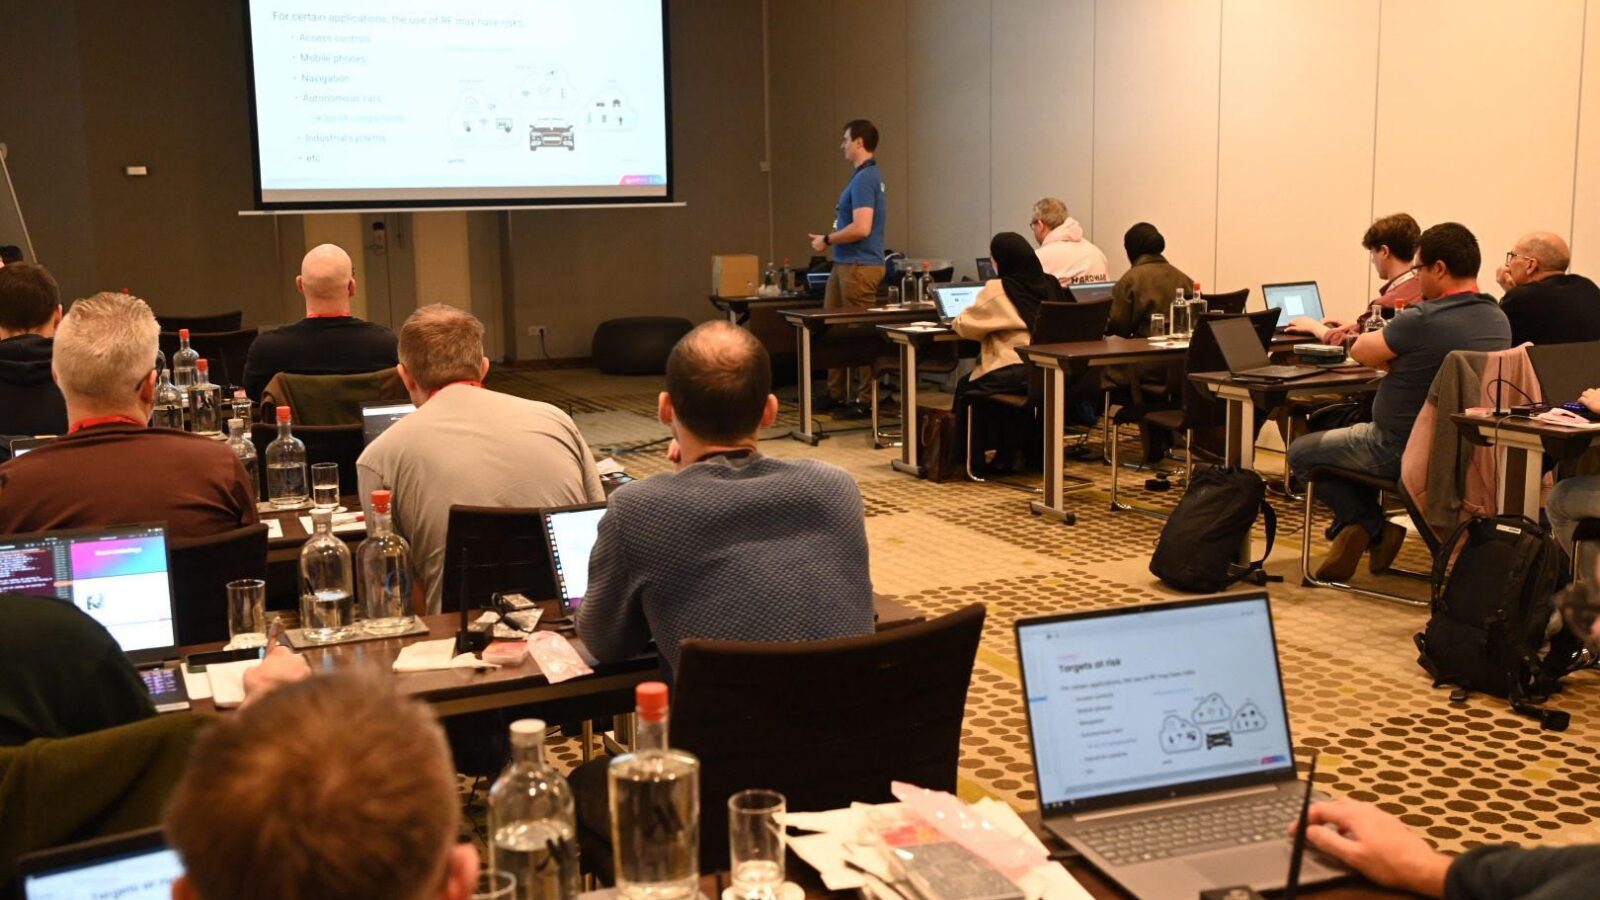
Built around your stack: baseband fuzzing, Wi-Fi protocol stacks, advanced RFID and NFC with SDR, hardware attacks on embedded systems, and other technologies.
Conferences where we have taught
Our courses have run at these conferences, and most of them can also run privately for your team.
Tailored trainings
Private training content is arranged around your needs: baseband attacks and fuzzing, Wi-Fi protocol stacks, advanced RFID and NFC with SDR, hardware attacks on embedded systems, and other technologies on request. Discounts scale with the number of attendees.
Public sessions in 2026
Sessions we run at conferences. You register through the event.
| Nov 16-18, 2026 | Hardwear.io NL 2026SDR Hacking Advanced: reversing and exploiting wireless communications |
Training for your team
We quote per group rather than per seat. Sessions run on your site, at our offices near Paris, or remotely with the kits sent in advance.