

RFID and NFC access control
We test the badges and cards, the readers and the controllers behind physical access: whether a credential can be cloned, replayed or forged, and whether the reader and the controller really check anything.
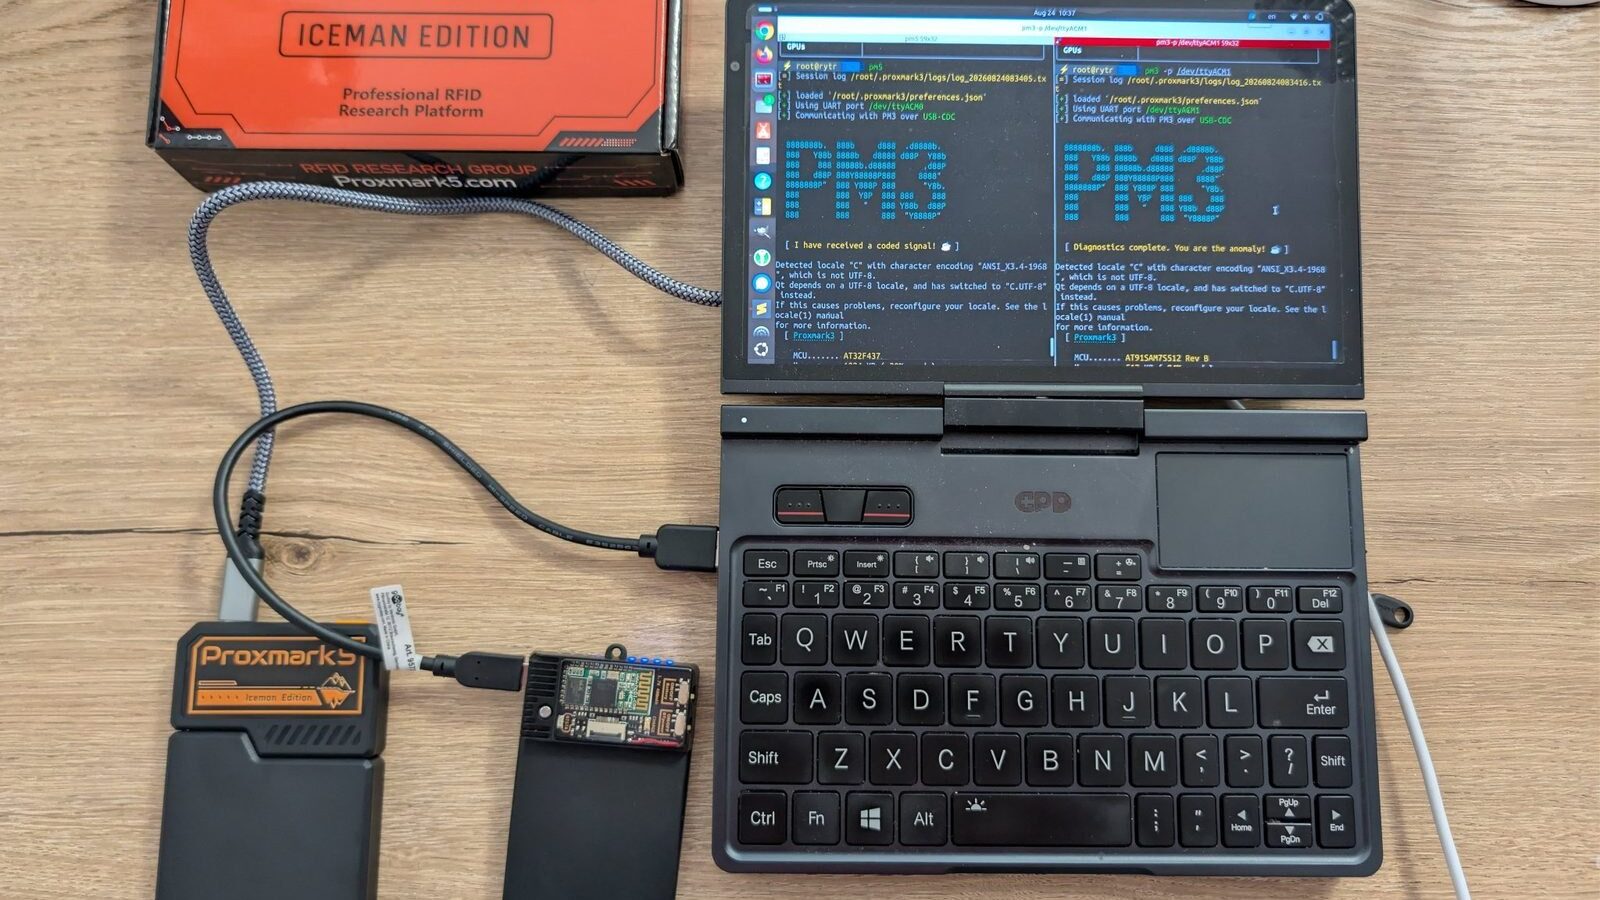
What an attacker could do
We check it before they do, with the same equipment.
Clone a badge
Copy a credential and walk through the door.
Replay an open
Replay a captured exchange to open a gate or a lock.
Forge a card
Crack MIFARE Classic, Ultralight or DESFire and make a working card.
Go past the reader
Fool a reader that does not really check the credential, or reach the controller behind it and open the door from there.
What we test
- LF and HF badges and cards (MIFARE Classic, Ultralight, DESFire)
- Readers, controllers and the door behind them
- NFC in your products
- The full credential lifecycle
- The NFC and reader stacks: we hunt for the bugs a malicious card or tag could use to crash or take over the reader, or the phone
How to work with us
The MIFARE attacker playbook: what three papers and one Proxmark3 teach you
RFID secrets with ICopy-X: iClass SE, secret of tags, teardown and more
Hack RFID fast with ICopy-X during Red Team engagements
IoT Hacking – the case of Intercoms (with little updates since 33C3)
Intercoms Hackings, when frontdoors become backdoors (more detailed)
House intercoms attacks, when frontdoors become backdoors (including progresses on 3G intercoms)
Trainings on this subject
All trainings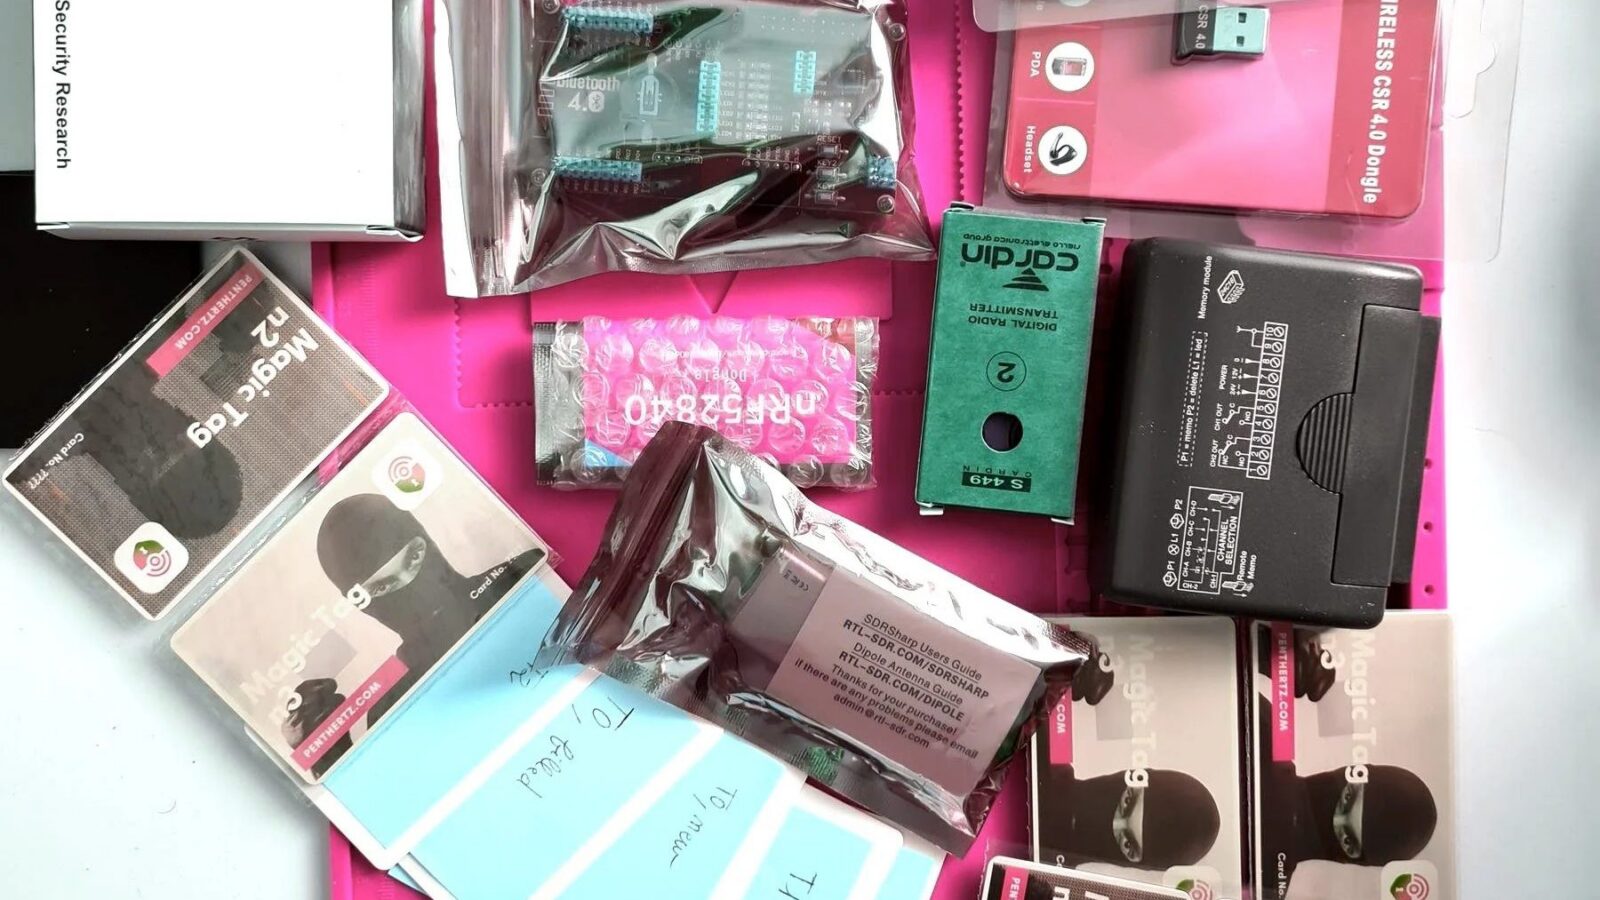
Three days on current attacks against the RFID, NFC, Bluetooth LE, nRF and sub-GHz systems met on pentests and red team engagements, to test access control and the radio links behind it.
Open doors stealthily with concrete techniques, and bypass most physical security systems that rely on RFID tags.
Talk to us about your project
We scope the work in a first call, then send a fixed-price proposal: intrusion tests, vulnerability research, fuzzing, test benches, trainings. Offices near Paris, Monday to Friday, 9:00 to 19:00.